
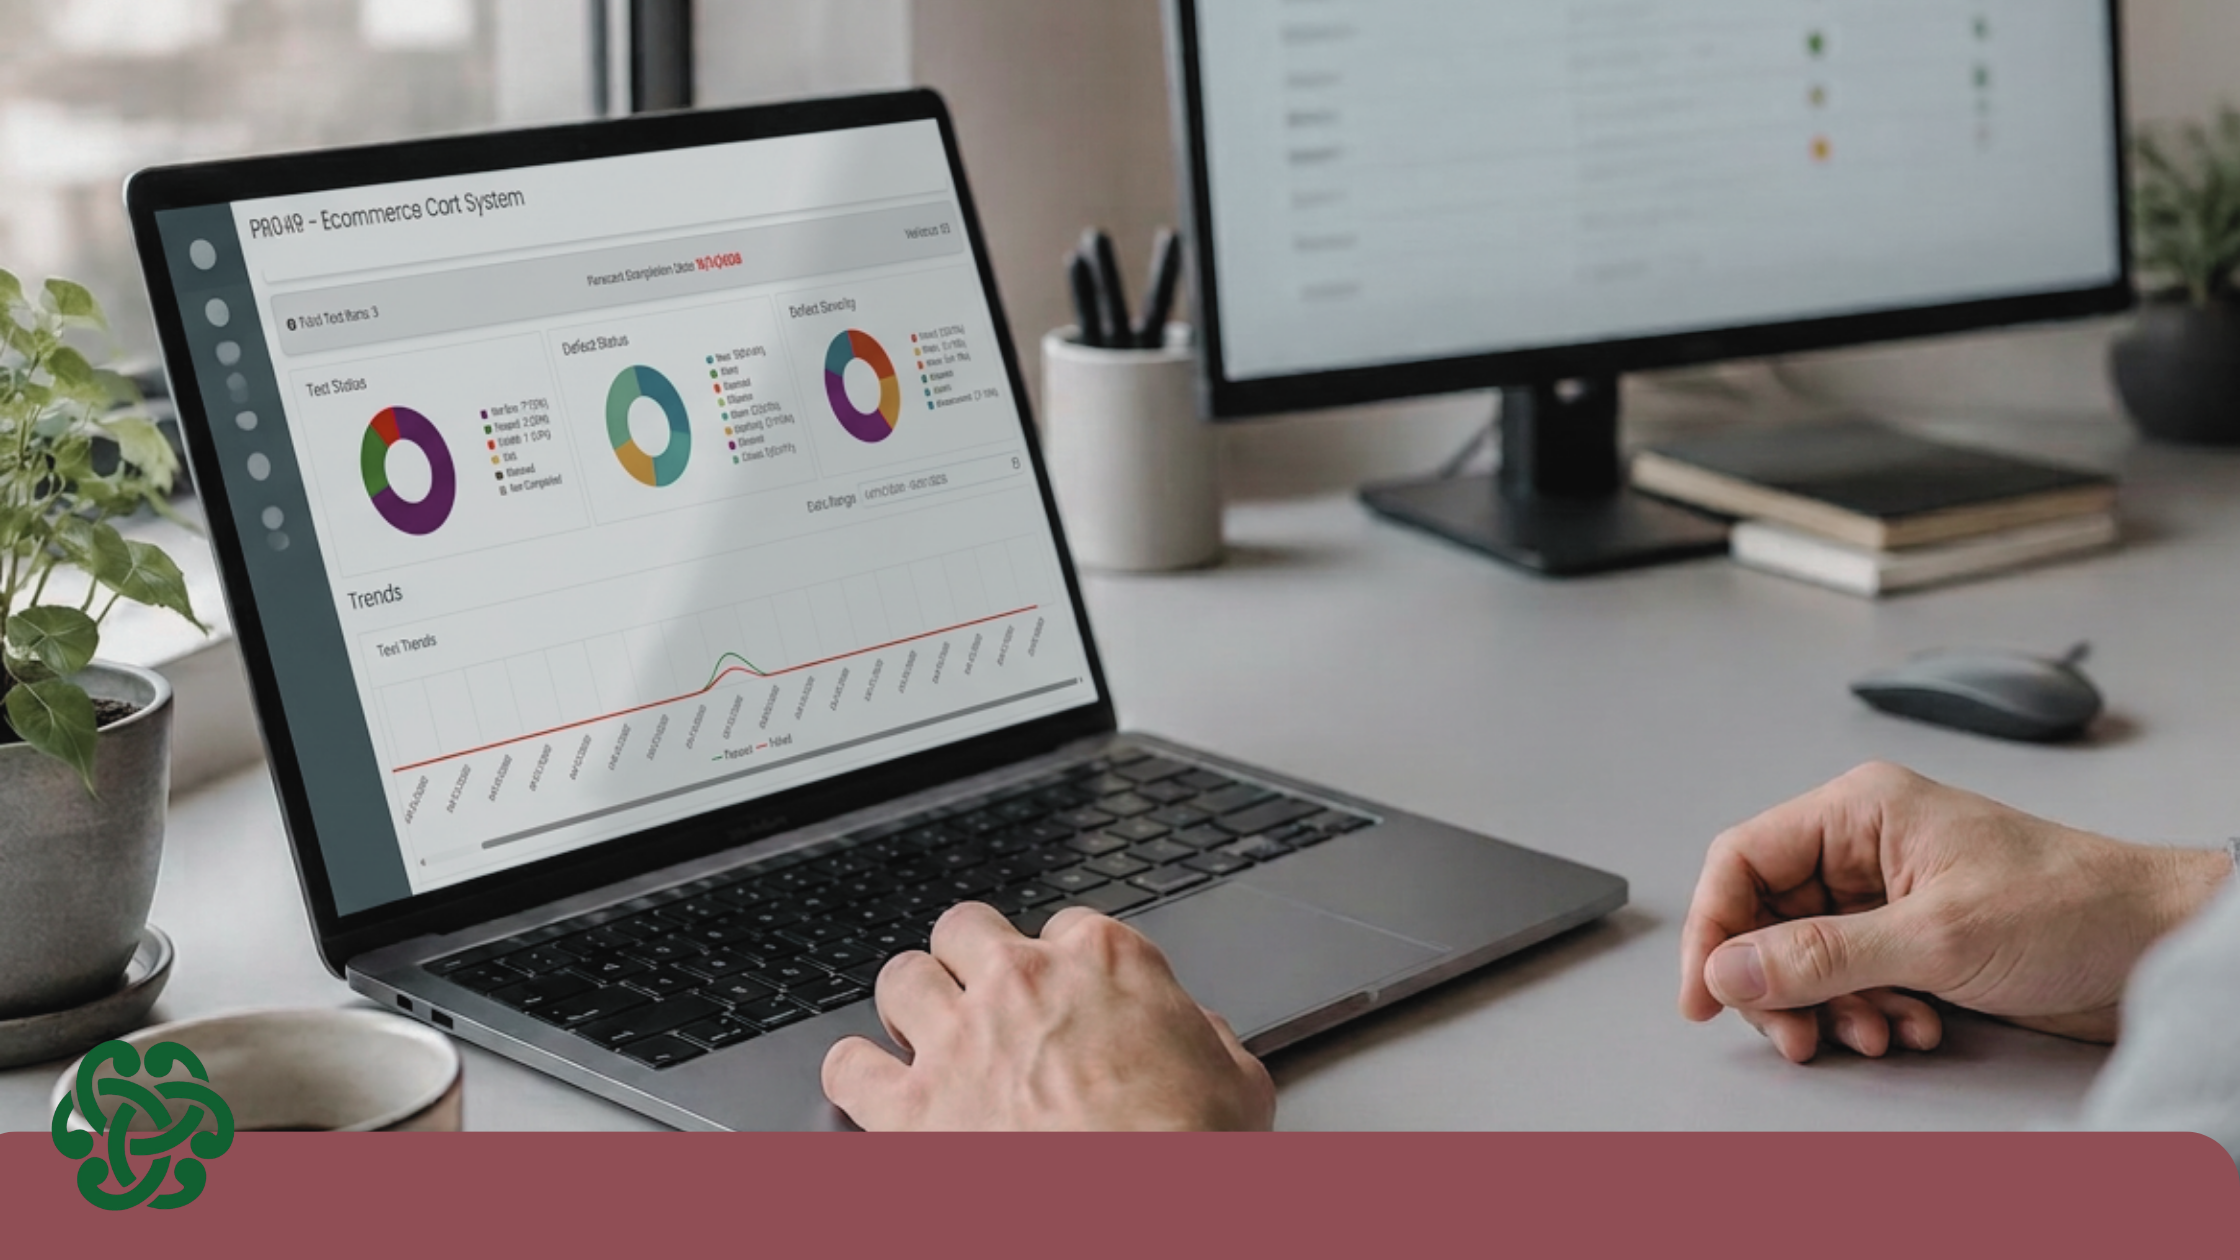
Test coverage measures how much of what matters in your software has been tested: requirements, high-risk workflows, positive and negative scenarios, automation, and actual execution. It’s not a single percentage. Measured properly, it tells QA teams where the gaps are and tells leadership how much risk a release carries.
When 90% coverage still lets defects through
Every QA team has lived this one. The coverage report looks healthy. The regression suite is green. Then a customer finds a defect in a workflow nobody thought to test, or in an edge case that only shows up when something goes wrong.
The problem usually isn’t effort. It’s that “coverage” got reduced to one number, and that number measured the wrong thing. For QA teams, that means coverage reviews that don’t find real gaps. For CIOs, it means no reliable answer to a simple question: how well tested is this release?
This post breaks down what test coverage really means, the five types worth tracking, how to measure each one, and how to see them all in one place. If gaps in negative scenarios are your biggest worry, see how TestGen AI closes coverage gaps.
What is test coverage?
Test coverage is a measure of how much of a product’s intended behavior has been validated by tests. That covers requirements, business risks, and positive and negative scenarios. Code coverage measures which lines of code ran. Test coverage measures whether the right things were checked.
The ISTQB Glossary frames coverage as the degree to which specified items have been exercised by a test suite. The key word is specified. You decide what counts, so what you choose to measure is a strategic decision, not a tooling default.
Test coverage vs. code coverage
Code coverage and test coverage are often used interchangeably, but they answer different questions.
|
|
Code coverage |
Test coverage |
|
Question it answers |
Which lines of code ran during tests? |
Have we tested what the product is supposed to do? |
|
Measured against |
Source code |
Requirements, risks and scenarios |
|
Owned by |
Developers |
QA teams and QA leadership |
|
Blind spot |
Missing functionality, untested business rules |
Needs good requirements and traceability |
|
Useful for |
Finding untested code |
Judging release risk |
Both are useful. But a product can hit 100% code coverage and still miss a requirement entirely, because code that was never written can’t show up as uncovered.
The five types of test coverage that matter
- Requirements coverage: every in-scope requirement has at least one linked test.
- Risk coverage: your highest-risk workflows have the deepest testing.
- Scenario coverage: both positive and negative paths are tested.
- Automation coverage: repeatable, critical tests are automated.
- Execution coverage: the tests you planned actually ran against this build.
- Requirements coverage. This is the foundation. Formula: requirements with at least one linked test ÷ total in-scope requirements × 100. If a requirement has no test, nobody can say it works.
- Risk coverage. Not every requirement carries the same weight. Revenue-generating transactions, compliance processes and critical integrations deserve deeper testing than a settings page. Formula: high-risk requirements with full test depth ÷ total high-risk requirements × 100.
- Scenario coverage. This is where most gaps hide. Teams test the happy path well, but negative scenarios (invalid inputs, failed integrations, permission errors) get skipped when time runs short or when the subject matter expert who knows the edge cases isn’t available. Track positive and negative tests per requirement separately.
- Automation coverage. Formula: automated tests in the critical regression suite ÷ total tests in that suite × 100. High automation coverage on the right tests means coverage holds up release after release, not just when the team has time.
- Execution coverage. Planned coverage means nothing if the tests didn’t run. Formula: tests executed against the current build ÷ tests planned for this release × 100. This is the number that matters on release day.
How do you measure test coverage?
- Define scope. List the in-scope requirements for the release.
- Rank risk. Tag each requirement by business impact so you know where depth matters most.
- Link tests to requirements. Make sure every test traces back to the requirement it validates.
- Check both paths. Confirm each high-risk requirement has positive and negative tests.
- Track execution live. Watch execution coverage against the current build, not last week’s export.
- Report by type, not one number. Show all five coverage measures side by side.
Steps 3 and 5 are where spreadsheets break down. Traceability drifts as requirements change, and execution data is out of date by the time it’s pasted into a report.
Where coverage gaps hide
- Unlinked tests: tests exist, but nobody can say which requirement they cover.
- Missing negative scenarios: happy paths tested, failure paths skipped.
- Stale requirements: requirements changed, tests didn’t.
- Tool silos: For example: stories in Jira, defects in Azure DevOps, automation results in Ranorex, and no single view tying them together.
- Averages that hide risk: strong coverage on low-risk areas inflates the total while critical paths stay thin.
How QAConnector measures coverage in one view
QAConnector is a QA management platform built by QA professionals at CelticQA Solutions. It brings test planning, execution, automation and reporting together, which is exactly what multi-dimensional coverage needs.
TestGen AI fills scenario gaps
TestGen AI generates positive and negative test cases in minutes from a requirement document, an import or a prompt. That removes the manual authoring delays caused by waiting on stakeholders or SMEs, which is where most negative-scenario gaps come from.
Audit-Proof QA keeps traceability intact
Audit-Proof QA logs every test and makes every result traceable to its requirement. Requirements coverage stops being a quarterly spreadsheet exercise and becomes something you can see at any time.
Test Stack Integration brings the data together
With Test Stack Integration, QAConnector connects with Jira, Azure DevOps, Ranorex, and many other test automation tools, so requirements, defects and automation results feed one source of truth.
Real-Time Reporting shows execution as it happens
Real-Time Reporting gives live visibility into test progress, defects and trends, with no delays and no filters. Execution coverage reflects the build you’re about to ship. For how this feeds a go/no-go decision, see our post on release readiness reporting.
See the coverage view in detail: explore Real-Time Reporting.
The CIO view: what coverage should tell leadership
The QA team owns the measurement. The CIO owns the risk. Coverage reporting earns its keep when it answers leadership questions directly:
- Are our highest-risk workflows fully tested? Risk coverage, not an overall average.
- What wasn’t tested, and why? Gaps shown, not hidden in a percentage.
- Can we prove it? A traceable record for SOX, NIST and ISO reviews.
- Is the platform secure? QAConnector is built on Microsoft Azure for enterprise-grade security, reliability and compliance.
Test Better = Save Money + Time. When coverage is measured properly, rework drops and release decisions get faster.
FAQ:
What is a good test coverage percentage?
There’s no universal target, because the right number depends on risk. Aim for full requirements coverage on in-scope features and full positive-and-negative scenario coverage on high-risk workflows. A lower overall percentage with complete risk coverage is safer than a high average that leaves critical paths thin.
Is test coverage the same as code coverage?
No. Code coverage measures which lines of source code ran during testing. Test coverage measures whether requirements, risks and scenarios were validated. A product can have high code coverage and still miss a requirement, because functionality that was never built can’t appear as uncovered code.
How do you calculate requirements coverage?
Divide the number of in-scope requirements with at least one linked test by the total number of in-scope requirements, then multiply by 100. The calculation only works if tests are reliably traced to requirements, which is why a QA management platform with built-in traceability makes it far easier to maintain.
Does 100% coverage mean no bugs?
No. Full coverage means every specified item was tested, not that every possible defect was found. Coverage shows where you’ve looked. Test quality, negative scenarios and realistic test data decide how much you find. Treat coverage as a risk signal, not a guarantee.
How do you improve test coverage quickly?
Start with your highest-risk requirements and check for missing negative scenarios, since that’s where gaps cluster. Link existing tests to requirements to expose blind spots. TestGen AI in QAConnector generates positive and negative test cases in minutes, so gaps get closed without waiting on SMEs.
Who should own test coverage reporting?
The QA manager or QA lead typically owns coverage measurement and reporting, with input from product owners on requirement scope and risk. Leadership, including the Head of Quality or CIO, should receive a summary by coverage type, especially risk coverage, before each major release.
Conclusion
Test coverage isn’t one number. It’s five: requirements, risk, scenarios, automation and execution. Measured together, they show QA teams exactly where the gaps are and give CIOs an honest answer about release risk.
Ready to see all five in one real-time view? Schedule a demo of QAConnector. If your team wants hands-on help building a coverage strategy, our parent company’s CelticQA Solutions QA Strategy services can work alongside you.
Recent Comments